Remedy Blog
Web3 security blog by the Remedy community.
Featured
Post-Deployment Smart Contract Monitoring: Where DeFi Actually Lost Money in 2026
An audit describes one commit on one day. What the 2026 loss data says about the smart contract risk that arrives afterwards, and how to evaluate the monitoring that covers it.
Read moreArticles
Stop waiting for clients to find you
Nearly every security researcher runs the same playbook: climb the contest leaderboard and wait. That only reaches projects who already know they need an audit. Most of them don't. If you're a web3 security researcher waiting for clients to come to you, you're competing for the smallest slice of the market. It's rarely that they can't afford one. Teams that skip an audit don't think they need one yet, or they believe their current version is safe. Meanwhile most auditors sit in the same box, grinding contest platforms and waiting for the leaderboard to send someone their way. That box only reaches projects who already know they need security and have already been through several audits. Everyone else, which is most of the market, never enters your funnel.
Lido V2 Audit: Critical Flaw Caught Before Launch
Inside Hexens' Lido V2 audit: 25 findings, 1 critical way to steal ETH by bypassing the withdrawal discount factor, and why manual review caught what scanners can't.
MainStreet Project "Autopsy" Report: msUSD and msY Token Depeg Incident
How MainStreet's msUSD and msY tokens depegged 96%: the mint/arbitrage mechanism, off-protocol USDC redeployment, and $23M in Morpho bad debt.
Inside a Native Rust Solana Audit: Security Pitfalls Every Builder Should Know
Five real vulnerabilities from a Native Rust Solana audit: account type confusion, CPI validation gaps, and unsafe closes, with fixes every builder needs.
The Smoke Detector Problem: What On-Chain Monitoring Can and Can't Stop in 2026
Detecting an attack is largely solved. Stopping it depends entirely on the attack's shape — and on whether a response was wired before the alarm fired.
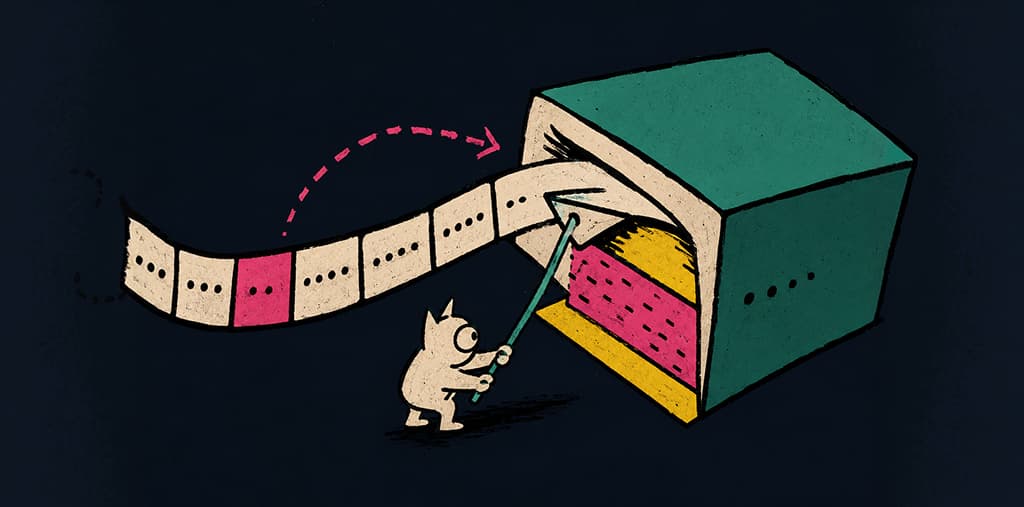
Understanding ABI Encoding for Dynamic Bytes in Solidity
A byte-by-byte walkthrough of ABI encoding for dynamic bytes in Solidity: what the offset, length, and data chunks actually mean in raw calldata.
I Was Out-Hunted by My Own AI: Where Human Researchers Still Win and How to Make It Count
A bug hunter on where AI now beats humans in smart contract security, breadth, depth, and bug combinations and where human judgment still wins. Featuring Grego AI.
Rust Compiler For Dummies
A beginner-friendly walkthrough of the Rust compiler: how source code becomes binary through lexing, AST, HIR/THIR, MIR borrow checking, and LLVM code generation.
Ethereum vs Solana: How Execution Models Shape Smart Contract Bugs
Ethereum vs Solana from a security researcher's lens: how the EVM's shared-ledger model and Solana's account-based runtime shape completely different smart contract bugs.
Polygon zkEVM Security Review: Four Critical Findings Fixed
Hexens' Polygon zkEVM security review found 16 issues, 4 critical, from missing PIL constraints to an ERC-777 bridge re-entrancy.
Taiko Bridge Exploit Headlines a $340M Year for Bridge Hacks
Taiko bridge exploit: an attacker used a Raiko SGX signing key exposed on GitHub to forge withdrawal proofs, adding to a $340M year of bridge hacks.
How to Detect Oracle Risk in Morpho Markets Using Glider
Hexens uses Glider's static analysis to flag four oracle misconfigurations in Morpho markets: hardcoded prices, stale feeds, and missing circuit breakers.